
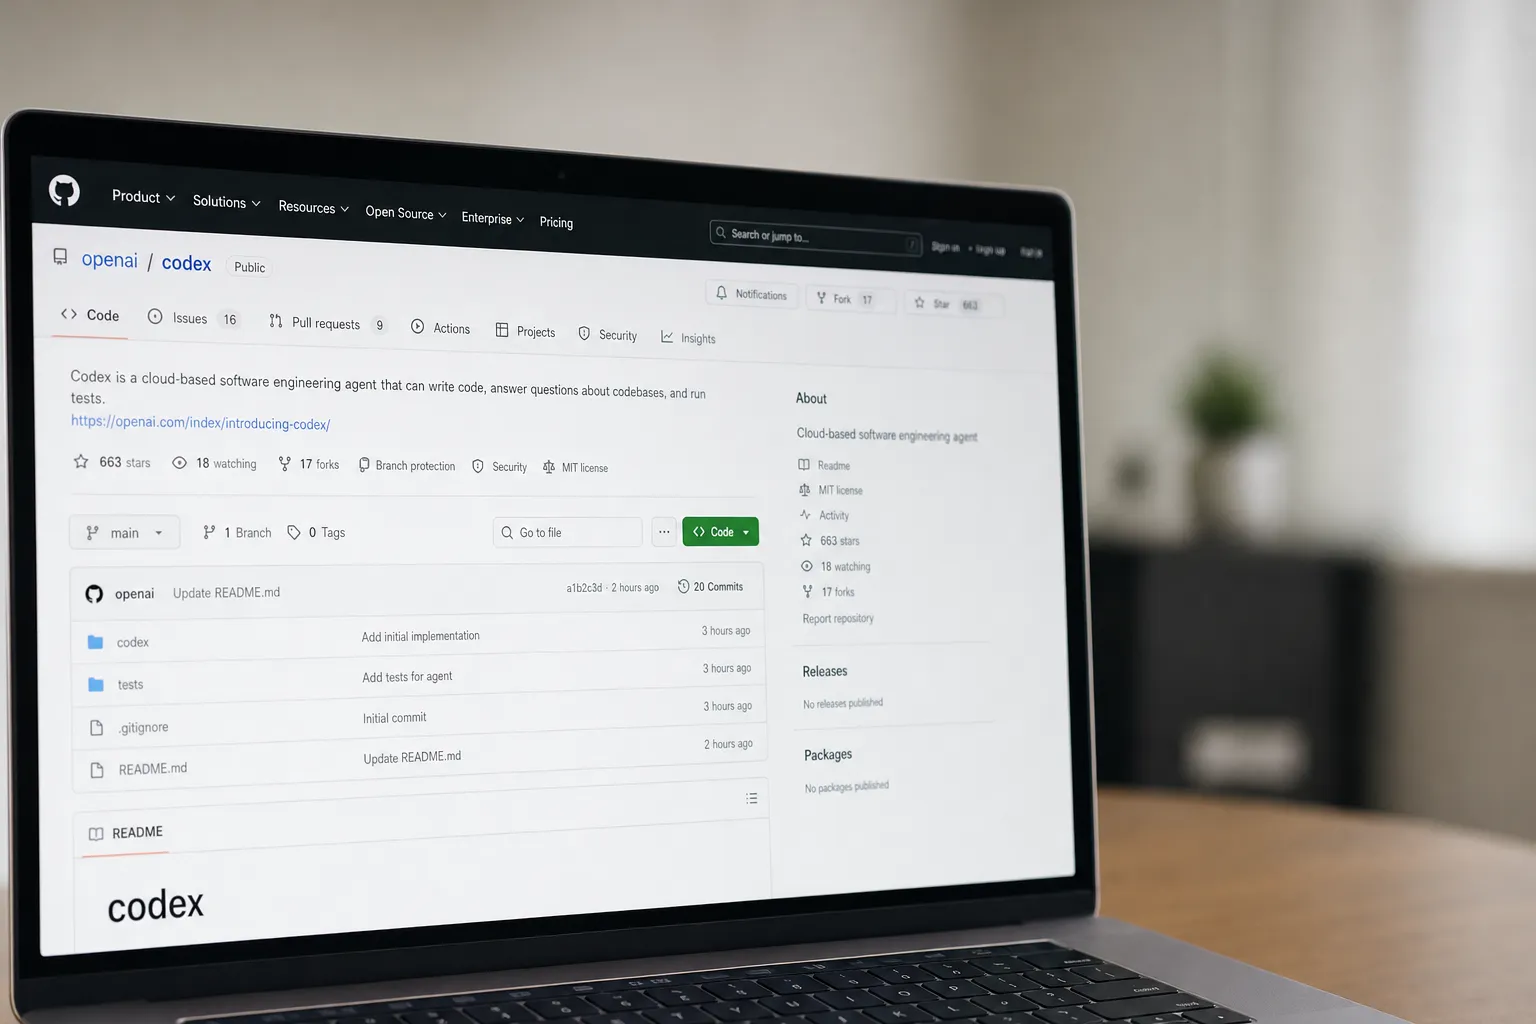
OpenAI's Codex Security, a command-line tool and TypeScript SDK designed for finding, validating, and fixing code vulnerabilities, surged 663 stars on GitHub in a single day this week, placing it among the platform's fastest-growing repositories. Created in mid-July 2026 and distributed via npm under an Apache 2.0 open-source license, the tool represents OpenAI's expansion into practical developer tooling beyond large language models. It leverages OpenAI's Codex engine—the same technology that powers GitHub Copilot and underpins Codex's code understanding capabilities—to provide AI-driven vulnerability analysis. The scale of the GitHub surge reflects both OpenAI's significant brand recognition in developer communities and genuine practical interest in how AI can improve security workflows. One day's star count is an imperfect adoption metric, but it does signal that developers are actively exploring this emerging category of AI-powered security tools.
The surge reflects broader developer appetite for AI-powered security tools entering the DevSecOps space. Established competitors like Snyk and Semgrep have built large user bases by automating scanning in developer workflows, but OpenAI's entry signals that the category is expanding to include AI-driven solutions. Meanwhile, other developer tools continue gaining traction on GitHub—the week saw strong interest in diverse categories from download managers to web performance guidance, suggesting developers are actively upgrading their tooling infrastructure across multiple domains. Codex Security's combination of CLI tooling and an npm SDK suggests a developer-first positioning; the Apache license and open npm distribution contrast with many enterprise security vendors' gated models, potentially lowering adoption barriers for open-source projects and smaller teams. What remains unclear: which vulnerability types the tool prioritizes, what detection accuracy it achieves compared to existing tools, and whether enterprises will integrate it into their security workflows at scale. These unknowns make the GitHub surge a signal of developer interest rather than confirmed production adoption.
The momentum is significant but its long-term implications remain unclear. GitHub stars measure initial developer interest, not production adoption or comparative effectiveness—critical questions for security tooling. It is not yet known whether the initial enthusiasm converts to sustained real-world usage in CI/CD pipelines, how well Codex Security performs against standard vulnerability benchmarks, or whether enterprises will adopt it at scale. The DevSecOps market remains competitive, with dozens of specialized tools competing for integration into developer workflows—vendors like Snyk and Semgrep have years of established track records. OpenAI's Codex Security holds clear advantages in brand recognition and AI capability, but these do not automatically translate to market dominance. The tool's young trajectory (122 days old since launch) will likely serve as a case study in how quickly AI-powered developer tools can gain traction on GitHub—and whether developers ultimately prioritize advanced AI-driven capabilities over the predictability of established vendor solutions and long-term support track records.